The rapid evolution and widespread accessibility of artificial intelligence have fundamentally transformed the global digital threat matrix, effectively industrializing cybercrime across the Asia-Pacific region. According to the seventh edition of the 2026 Cyber Threat Landscape Report published by Ensign InfoSecurity, malicious actors are increasingly weaponizing artificial intelligence to automate and dramatically accelerate malicious operations. From sophisticated reconnaissance and automated vulnerability scanning to the generation of hyper-personalized, highly convincing phishing lures, AI has lowered the technical barrier to entry for cybercriminals while exponentially increasing the scale, speed, and precision of their attacks.
This technological convergence has triggered a profound shift in regional cybersecurity dynamics, particularly within the Association of Southeast Asian Nations (ASEAN) member states. As criminal syndicates adopt enterprise-level efficiency models—complete with automated attack pipelines and AI-driven social engineering—traditional defensive paradigms are proving inadequate. Security analysts note that the democratization of advanced machine learning tools allows threat actors to orchestrate multi-layered assaults simultaneously across multiple jurisdictions, complicating attribution and overwhelming conventional incident response frameworks.
The escalating threat landscape poses severe national security and economic challenges, none more pronounced than in Indonesia. Recent empirical data underscores an unprecedented digital emergency within Southeast Asia’s largest economy. Official figures released by the National Cyber and Crypto Agency (BSSN) reveal that Indonesia recorded an astonishing 5.5 billion cyberattack activities throughout 2025. This figure represents a staggering surge—more than a sevenfold increase—when compared to the historical annual averages recorded between 2020 and 2024. The data illustrates a transition from sporadic, opportunistic hacking attempts to sustained, automated, and high-volume campaigns targeting critical infrastructure, financial institutions, and government networks.
Simultaneously, the human and economic cost of digital fraud has reached critical proportions. The Ministry of Communication and Digital (Kemenkomdigi) reported that cumulative financial losses suffered by Indonesian citizens due to digital scams and online fraud have surpassed IDR 7.5 trillion. These losses stem from an array of AI-enhanced schemes, including deepfake-enabled impersonation, synthetic identity fraud, and sophisticated investment scams distributed via compromised communication channels. The convergence of macro-level state and corporate infrastructure attacks with micro-level financial fraud highlights a systemic vulnerability within Indonesia’s digital ecosystem.
The Chronology of the Modern Threat Evolution
To understand the current crisis, it is necessary to examine the trajectory of cyber threats in the Asia-Pacific region over the past decade. Between 2020 and 2024, the region experienced a steady digitization wave accelerated by the COVID-19 pandemic. Remote work policies, cloud migration, and rapid e-commerce adoption vastly expanded the digital attack surface. During this initial phase, cybercrime remained largely manual, requiring specialized human labor for reconnaissance, credential harvesting, and social engineering. Ransomware-as-a-Service (RaaS) emerged as a dominant business model, yet operations were still bound by the operational bottlenecks of human attackers.
The inflection point occurred between late 2023 and 2025, marked by the mainstream commercialization of generative artificial intelligence and large language models. Cybercriminal ecosystems quickly co-opted these technologies, stripping away safety guardrails through illicit forums and customized dark-web tooling. By 2025, the utilization of AI transitioned from experimental novelties to baseline operational infrastructure for advanced persistent threat (APT) groups and financially motivated cyber syndicates alike.
This chronological shift culminated in the findings of the 2026 Ensign InfoSecurity report, which documents how AI-driven tools have compressed the cyberattack lifecycle. Tasks that previously required weeks of manual labor—such as mapping an organization’s network topology, identifying zero-day vulnerabilities, and crafting targeted spear-phishing campaigns in local languages—can now be executed in mere minutes. The industrialization of these processes means that threat actors can launch high-volume, highly customized attacks against thousands of targets simultaneously, rendering traditional perimeter defenses obsolete.
Expert Insights and Corporate Warnings
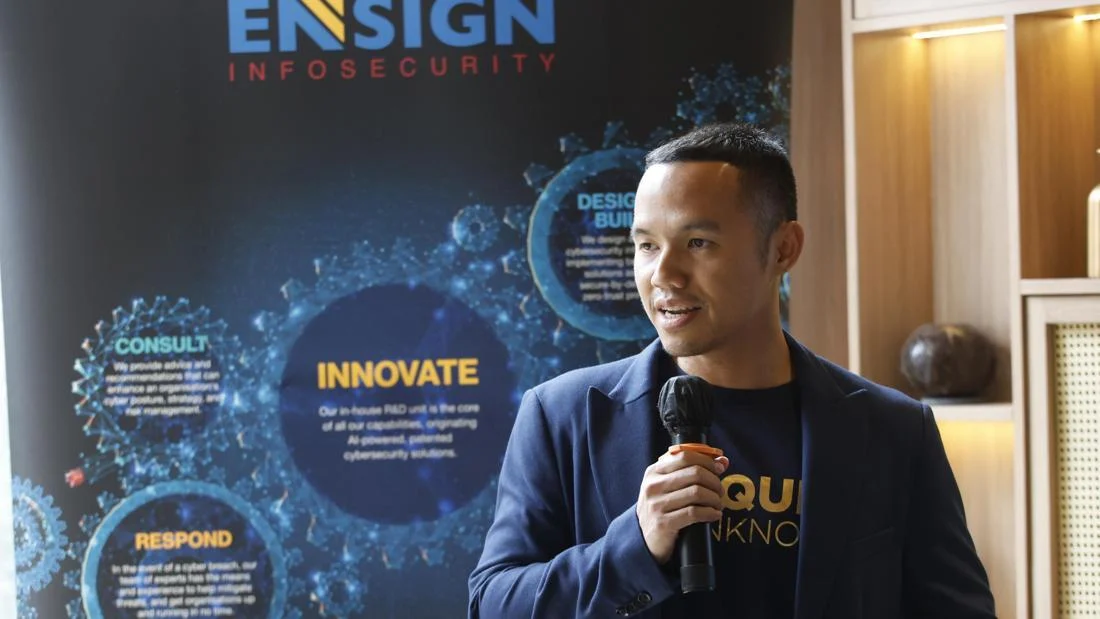
Addressing the media during a briefing in Jakarta on Wednesday, September 16, 2026, Adithya Nugraputra, Head of Consulting at PT Ensign InfoSecurity Indonesia, emphasized the alarming velocity of technological advancement within the threat actor community. According to Nugraputra, the cycle time for updates and capability enhancements in attacker-utilized AI models is approximately two months, outpacing the annual or semi-annual update cycles typical of corporate security software.
"Organizations can no longer rely on static security controls," Nugraputra stated firmly during the briefing. "It is imperative to prioritize continuous vulnerability scanning and the immediate application of patches on all assets connected to the internet. Furthermore, enterprises must regularly test their defensive postures against the latest iterations of adversarial AI models to ensure resilience."
Nugraputra’s analysis highlights a critical strategic mismatch: while corporate governance and bureaucratic procurement processes often slow down the adoption of new security tools, cybercriminal syndicates operate with the agility of modern tech startups, continuously integrating state-of-the-art machine learning capabilities into their offensive playbooks. This disparity creates a widening security gap that leaves unprepared institutions highly vulnerable to catastrophic breaches.
Broader Socio-Economic Implications and Regulatory Responses
The broader implications of this AI-accelerated threat landscape extend far beyond immediate corporate financial losses or data leaks. At a macroeconomic level, persistent cyber insecurity threatens to undermine foreign direct investment, disrupt supply chains, and erode consumer trust in digital commerce. For developing digital economies like Indonesia, where national growth increasingly relies on financial technology and digital transformation initiatives, pervasive cybercrime acts as a severe tax on innovation.
In response to the escalating crisis, regulatory bodies and government agencies are facing mounting pressure to overhaul national cybersecurity frameworks. BSSN, alongside the Ministry of Communication and Digital, has intensified calls for mandatory cybersecurity reporting, stricter data protection enforcement, and cross-border intelligence sharing within the ASEAN region. Cybercriminals routinely exploit jurisdictional boundaries, routing attacks through multiple neighboring countries to evade local law enforcement. Consequently, regional cooperation frameworks are vital to tracing illicit financial flows and dismantling the infrastructure supporting AI-driven scams.
Furthermore, public-private partnerships are emerging as a cornerstone of national defense strategy. Government bodies alone lack the real-time visibility into corporate network traffic required to counter automated, AI-driven incursions. Conversely, private enterprises possess the technical telemetry but frequently lack the authority or legal mandate to disrupt international criminal networks. Bridging this gap requires synchronized frameworks for information sharing, capacity building, and talent development. Indonesia faces a pronounced shortage of certified cybersecurity professionals, a vulnerability that complicates efforts to deploy and manage advanced AI-driven defensive systems.
Strategic Imperatives for Enterprise Defense
As the industrialization of cybercrime matures, cybersecurity experts stress that mitigation strategies must evolve from reactive remediation to proactive, intelligence-led defense. Organizations operating in Indonesia and the broader Asia-Pacific region are advised to adopt several foundational measures:
- Dynamic Security Posture Management: Moving away from periodic penetration testing toward continuous automated security validation. Because threat actors update their AI models bi-monthly, internal defenses must be tested with comparable frequency.
- Zero-Trust Architecture: Implementing strict identity verification protocols across all network layers. Assuming implicit trust based on network perimeter location is no longer viable when AI-generated credentials and deepfake communications can bypass traditional perimeter checks.
- AI-Enhanced Defensive Tools: Leveraging artificial intelligence and machine learning within Security Operations Centers (SOCs) to detect anomalous behavior patterns at machine speed. Human analysts alone cannot process the volume of alerts generated in an era of automated attacks.
- Comprehensive Employee Resilience Programs: Upgrading security awareness training to account for generative AI capabilities. Employees at all levels must be educated on the realities of hyper-realistic phishing, synthetic voice cloning, and video-based deepfake manipulation during corporate communications.
The findings of the 2026 Cyber Threat Landscape Report serve as a stark reminder that the digital battlefield has fundamentally changed. As artificial intelligence continues to lower the cost and increase the velocity of cyberattacks, the future security of the region depends on the collective ability of governments, enterprises, and civil society to innovate faster than the adversaries threatening their digital sovereignty.
