The recent revelation by the Indonesian National Police’s Criminal Investigation Agency (Bareskrim Polri) regarding the alleged illegal wiretapping of President Prabowo Suboanto has thrust a sophisticated surveillance infrastructure into the public spotlight. At the center of this high-profile security breach is the Lawful Interception Management System (LIMS), a technology inherently designed for legitimate law enforcement operations but allegedly subverted for unauthorized monitoring. The sprawling investigation, which came to light in late October 2026, has exposed vulnerabilities in telecommunication oversight, raising critical questions about institutional checks and balances, the boundaries of state surveillance, and the security of top-tier government officials in an increasingly digitized geopolitical landscape.
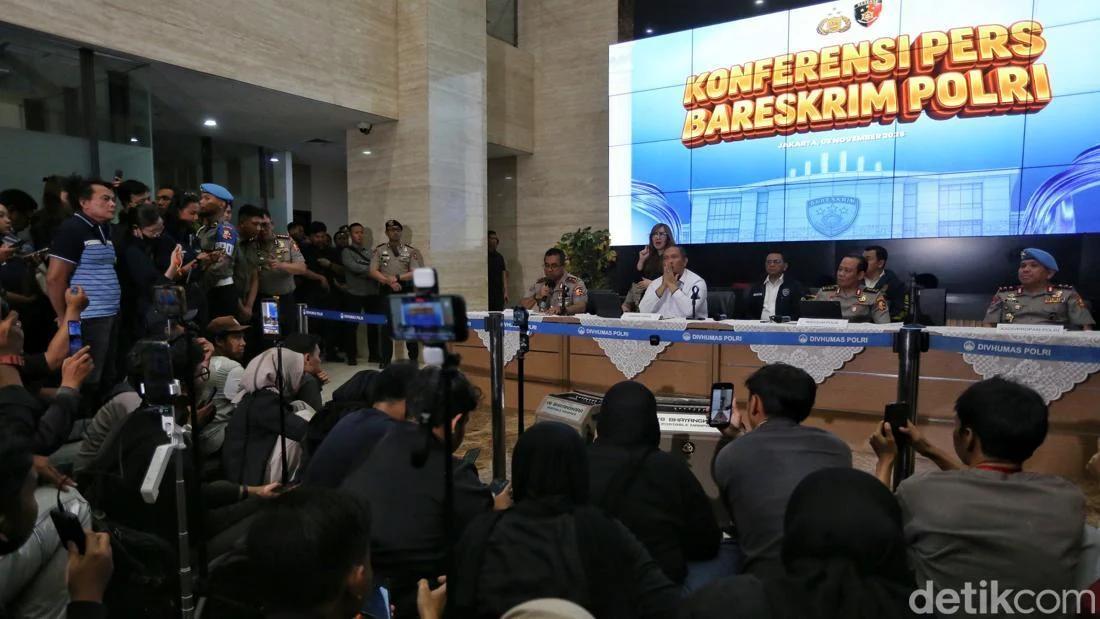
According to official statements delivered by Bareskrim Polri, the unauthorized wiretapping operations occurred throughout 2025 and 2026. Investigators discovered that multiple telephone numbers, notably including that of President Prabowo Subianto, were illicitly injected into the LIMS servers completely bypassing mandatory administrative checks, legal authorizations, and procedural verifications. Kabareskrim Polri, Commissioner General Asep Safrudin, detailed during a press conference in Jakarta that these insertions lacked the requisite formal request letters from authorized investigators as well as the accompanying police reports, pointing toward a calculated abuse of institutional authority.
Understanding Lawful Interception Management System (LIMS)
To comprehend the severity of the alleged misuse, one must understand the intended function of LIMS within modern telecommunications ecosystems. Lawful Interception Management System is an advanced framework engineered to facilitate authorized communications interception by designated law enforcement agencies and national security bodies. Fundamentally, it serves as the operational nexus for lawful interception—a legally mandated process wherein telecommunication service providers must grant authorized state institutions the technical capability to intercept communications for the prevention and investigation of serious crimes.
Global telecommunication standards, such as those established by the European Telecommunications Standards Institute (ETSI), define lawful interception architecture comprehensively. Under guidelines like ETSI TS 104 007, a compliant interception system must incorporate strict authorization workflows, specific target provisioning, secure information extraction mechanisms, and dedicated delivery channels for transmitting intercepted data to authorized monitoring facilities. Furthermore, academic and institutional assessments, including a 2025 research paper by the European Parliamentary Research Service (EPRS), emphasize that lawful interception systems are capable of capturing two distinct categories of data: Content of Communication (CC) and Intercept-Related Information (IRI).
Content of Communication refers to the actual substance of the intercepted transmission, such as voice conversation audio, text contents, or multimedia exchanges. Conversely, Intercept-Related Information comprises rich metadata, encompassing the identities of communicating parties, connection timestamps, routing details, and network-based geographical location data. LIMS acts as the administrative and technical engine that manages these streams, bridging the gap between massive telecommunication carrier infrastructures and the analytical terminals of state authorities.
The Technical Mechanism: How LIMS Operates Without Target Detection
One of the most alarming aspects of network-level interception technologies like LIMS is their operational discretion. Unlike malicious software, commonly known as spyware or Pegasus-style payloads that require covert installation onto a target’s physical smartphone, a network-based lawful interception system operates at the infrastructure level of the telecommunication provider.
When an intercept is legally sanctioned, requests flow through rigid bureaucratic and cryptographic authorizations, activating specific intercept facilities residing within the core networks of telecom operators. Because the interception occurs upstream—routing packets or duplicating voice circuits directly from the telecommunications carrier switches before they reach the public network—the target device does not require any malicious applications installed. Consequently, the user receives no notifications, unusual battery drains, or system anomalies that typically accompany endpoint device compromises.
In the case involving the Indonesian presidency and other high-ranking targets, this infrastructure-level access meant that perpetrators could siphon both metadata and conversational content seamlessly, provided they possessed administrative privileges over the LIMS server environment. The absence of traditional digital footprints on the target devices highlights the profound risks associated with insider threats and the compromise of centralized surveillance control panels.
Chronology of the Investigation and Systemic Discovery
The unfolding scandal did not emerge overnight; rather, it represents the culmination of internal discrepancies noticed by diligent personnel within the security apparatus. The timeline of the investigation underscores the rapid response of law enforcement once the breach was formally documented:
- Throughout 2025 – Early 2026: The illicit wiretapping operations allegedly take place, during which multiple sensitive telephone numbers, including those belonging to state officials, political figures, media representatives, civil society leaders, and prominent business executives, are covertly entered into the LIMS servers without verification.
- Late October 2026: Suspects allegedly order the systematic deletion of captured wiretapping data files and system activity logs in an attempt to erase their digital footprints and obstruct future auditing.
- October 30, 2026: An institutional whistleblower or observant security officer files an official police report, initiating the formal criminal investigation into the unauthorized surveillance activities.
- November 3, 2026: Bareskrim Polri holds a high-profile press conference in Jakarta. Kabareskrim Commissioner General Asep Safrudin publicly reveals the systemic flaws, the circumvention of verification protocols, and the scope of the unauthorized surveillance targeting the nation’s highest leadership.
During the preliminary phase of the investigation, Bareskrim investigators acted swiftly to secure physical and digital evidence. Authorities interrogated at least 10 key witnesses and consulted three independent technical experts specializing in telecommunications security and digital forensics. Furthermore, law enforcement seized critical material evidence, including 11 cellular phones, one iPad tablet, and four flash memory drives containing potential digital artifacts and system logs.
Legal Repercussions and Suspect Identification
As the evidentiary web tightened, Bareskrim Polri formally named three primary suspects linked to the operation and management of the compromised LIMS infrastructure. The individuals implicated in the scandal include former Indonesian National Police Chief (Kapolri) Listyo Sigit Prabowo, along with Ahrie Sonta Nasution and Eko Hadi Santoso.
Despite the gravity of the charges and their high profiles, judicial proceedings adhere strictly to the principle of the presumption of innocence. As of the current legal phase, the named suspects remain under active investigation and have not been formally pronounced guilty by a court of law. They continue to undergo rigorous legal scrutiny as prosecutors and investigators build a comprehensive case regarding the unauthorized access, abuse of power, and intentional destruction of digital evidence.
Broader Implications for National Security and Digital Governance
The alleged weaponization of the Lawful Interception Management System against the head of state and other influential figures carries profound implications for Indonesia’s national security framework and the broader landscape of digital governance. First, it exposes a critical vulnerability in the oversight mechanisms governing state surveillance tools. When technologies engineered to protect national security are perverted through administrative bypasses and a lack of multi-factor authorization, they transform from shields into instruments of political espionage.
Second, the wide-ranging target list—encompassing not only the president but also senior government ministers, opposition or allied political figures, journalists, non-governmental organizations, and prominent business leaders—points to a systemic erosion of privacy rights. This revelation is expected to trigger sweeping legislative and institutional audits regarding how telecommunication providers interface with law enforcement agencies, forcing the state to implement stricter cryptographic logging, immutable audit trails, and independent judicial oversight boards to oversee all lawful interception requests.
Ultimately, the LIMS controversy serves as a stark reminder that as nations digitize their infrastructure and adopt advanced intelligence technologies, the greatest threat often lies not in foreign cyberespionage, but in the institutional failure to secure domestic oversight mechanisms against internal abuse. As the legal proceedings against the suspects progress, the outcome will likely reshape the future of state surveillance regulations in Indonesia for decades to come.

